 Certia
Access reviews,done properly.
Practical, tool-agnostic guides for teams running user access reviews in Jira and Confluence for SOC 2 and ISO 27001 audits.
SOC 2 user access review in Jira Cloud: a step-by-step guide
Scope, find the direct grants a group-only review misses, record decisions with reasons, prove revocations, and package the evidence.
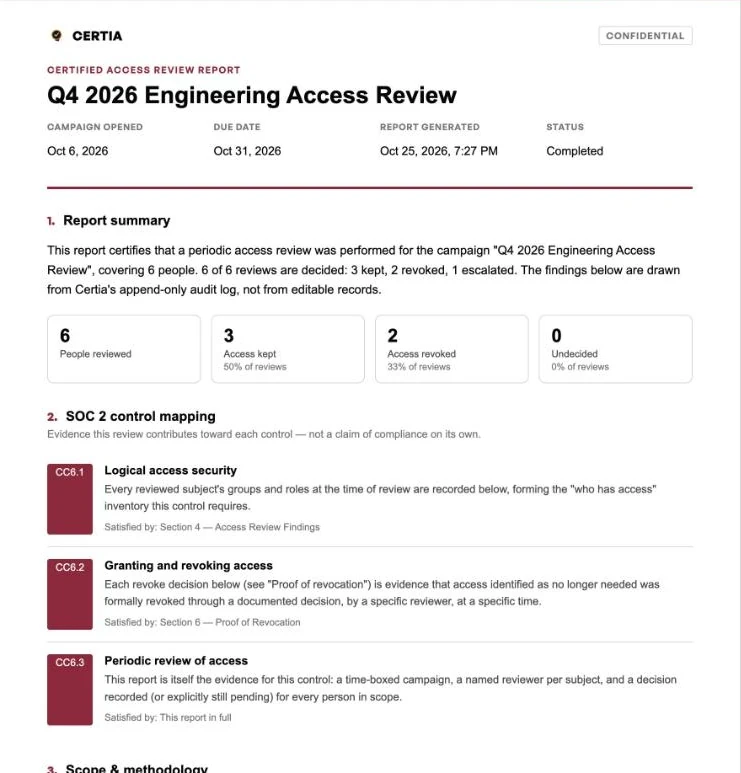 SOC 2
How to run a SOC 2 user access review in Jira Cloud
Scope, find the direct grants a group-only review misses, record decisions with reasons, prove revocations, and package the evidence.
Who actually has access to your Jira project?
Group membership vs. direct role grants, and why reviews miss the second.
Confluence space permissions audit
Finding direct space grants that bypass your groups.
What counts as evidence for CC6.2 and CC6.3
What an auditor accepts from an access review, and what they don't.
ISO 27001 A.5.18 access rights review for Atlassian Cloud
Running the Annex A access rights review on Jira and Confluence.
No guides on this topic yet.
Skip the spreadsheet next quarter.
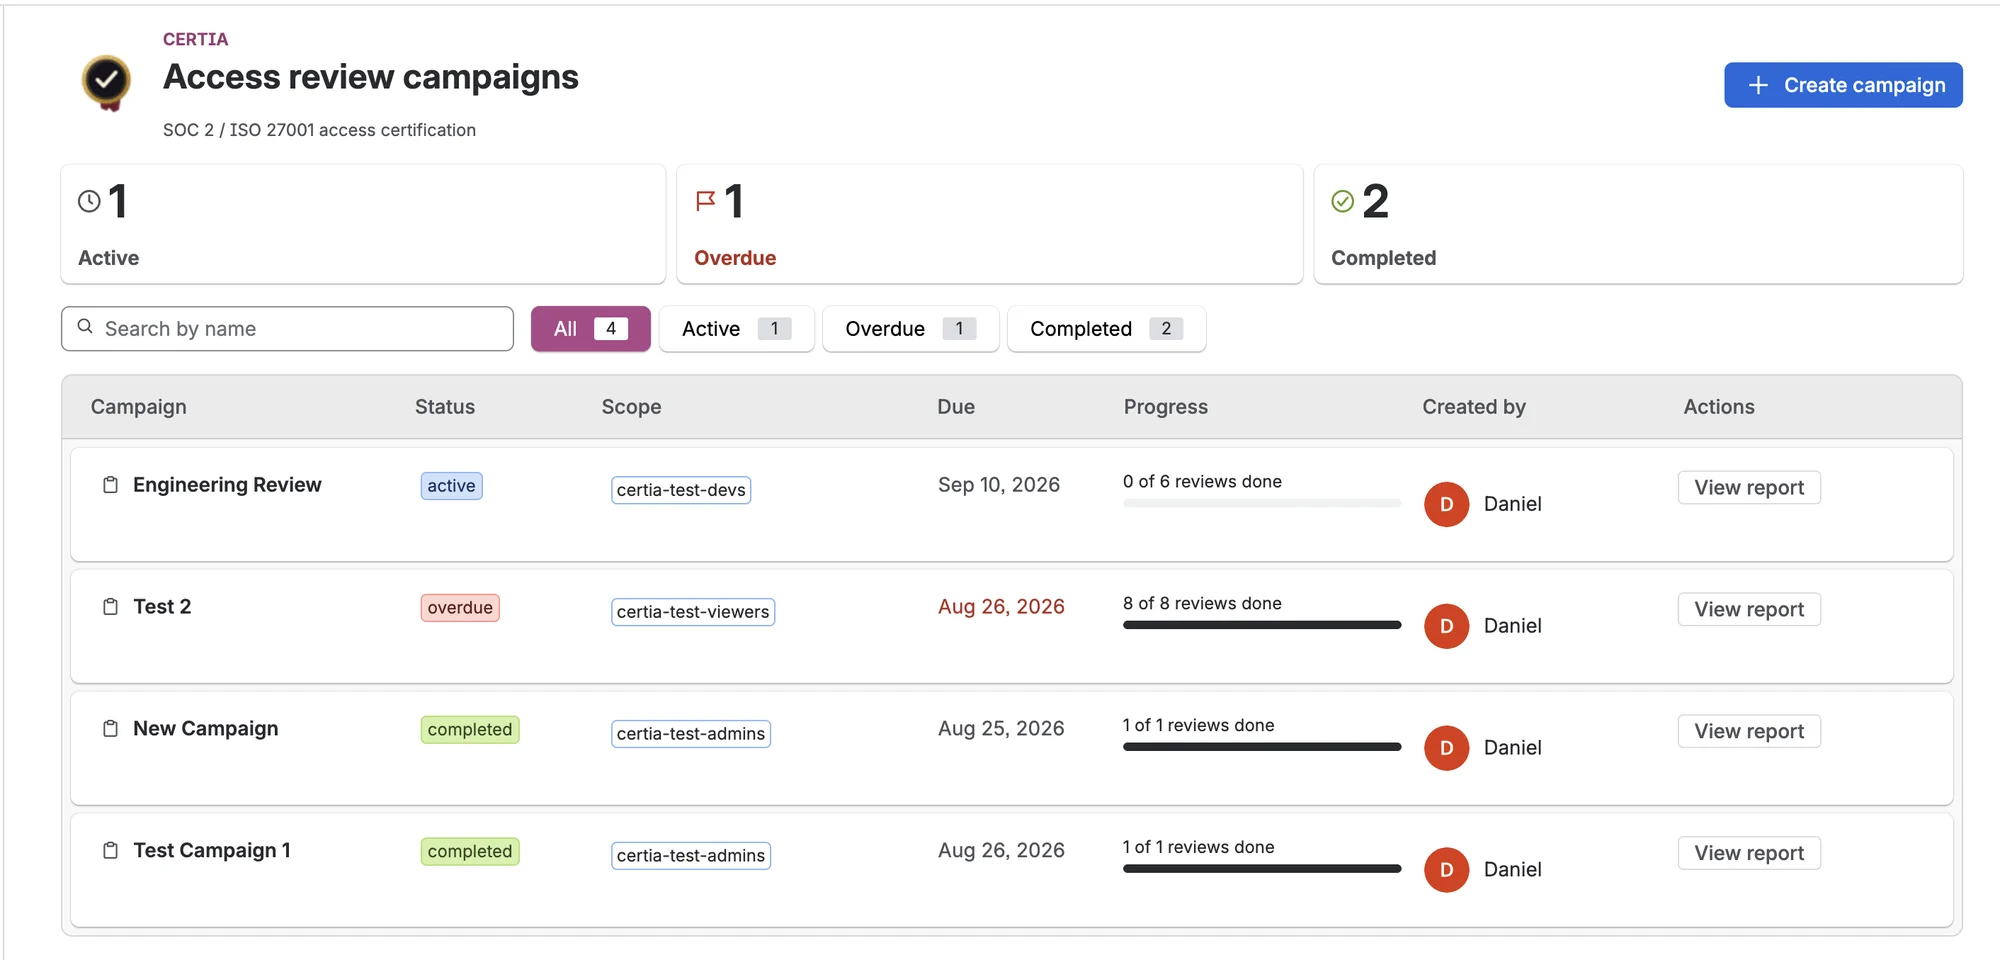
Certia runs the review these guides describe, inside Jira Cloud, and produces the record at the end.
more every month
How every Certia screen and report section works.